All Topics
XSS, CSRF & Client Attacks
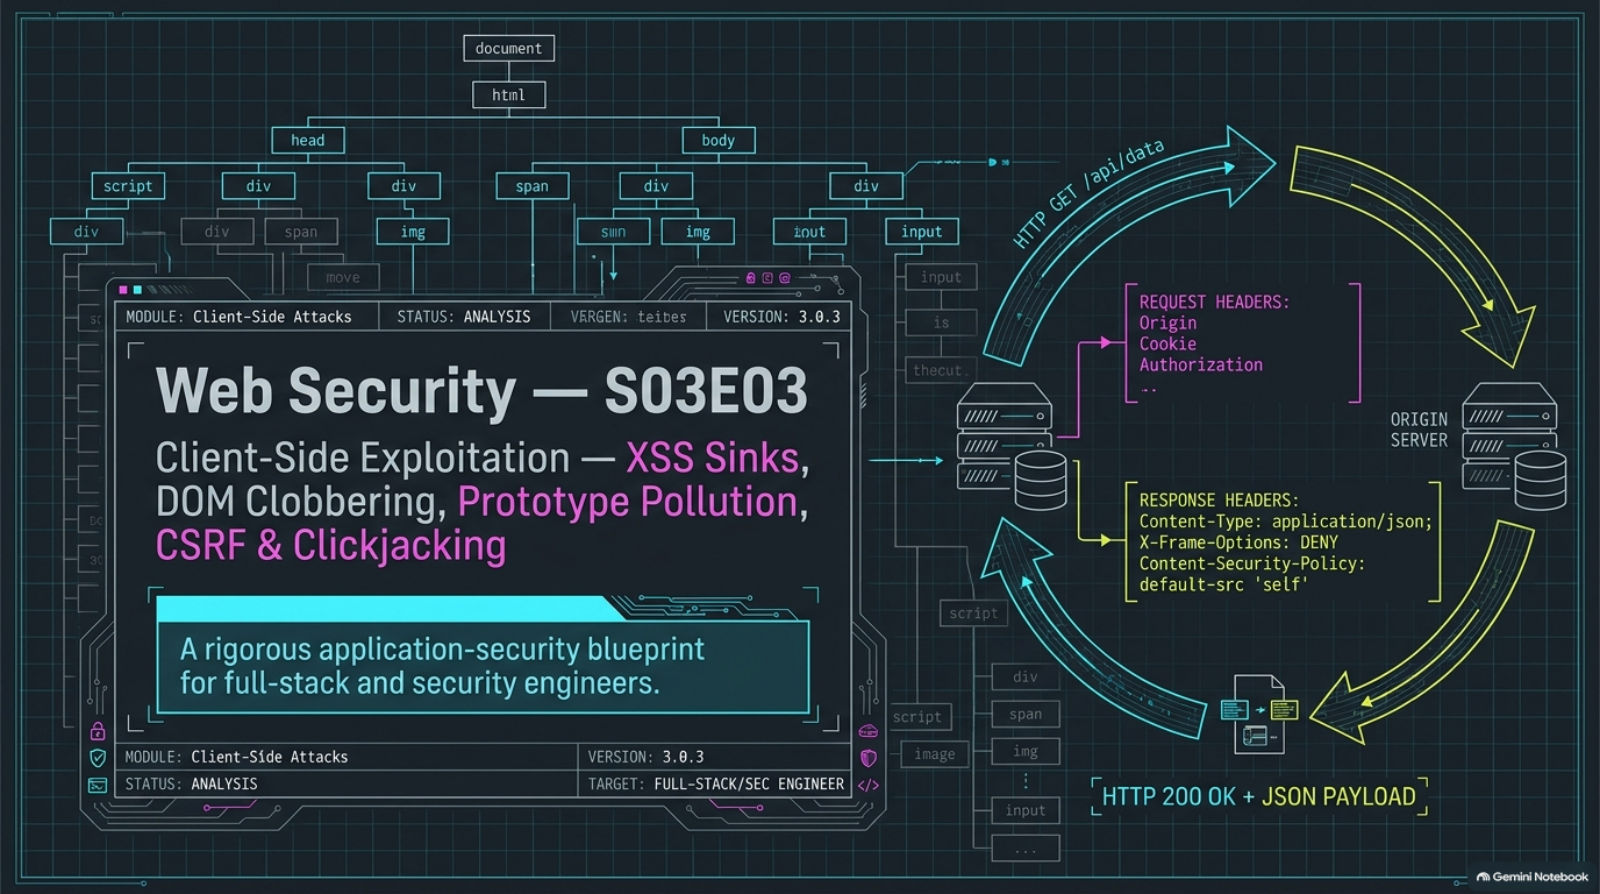
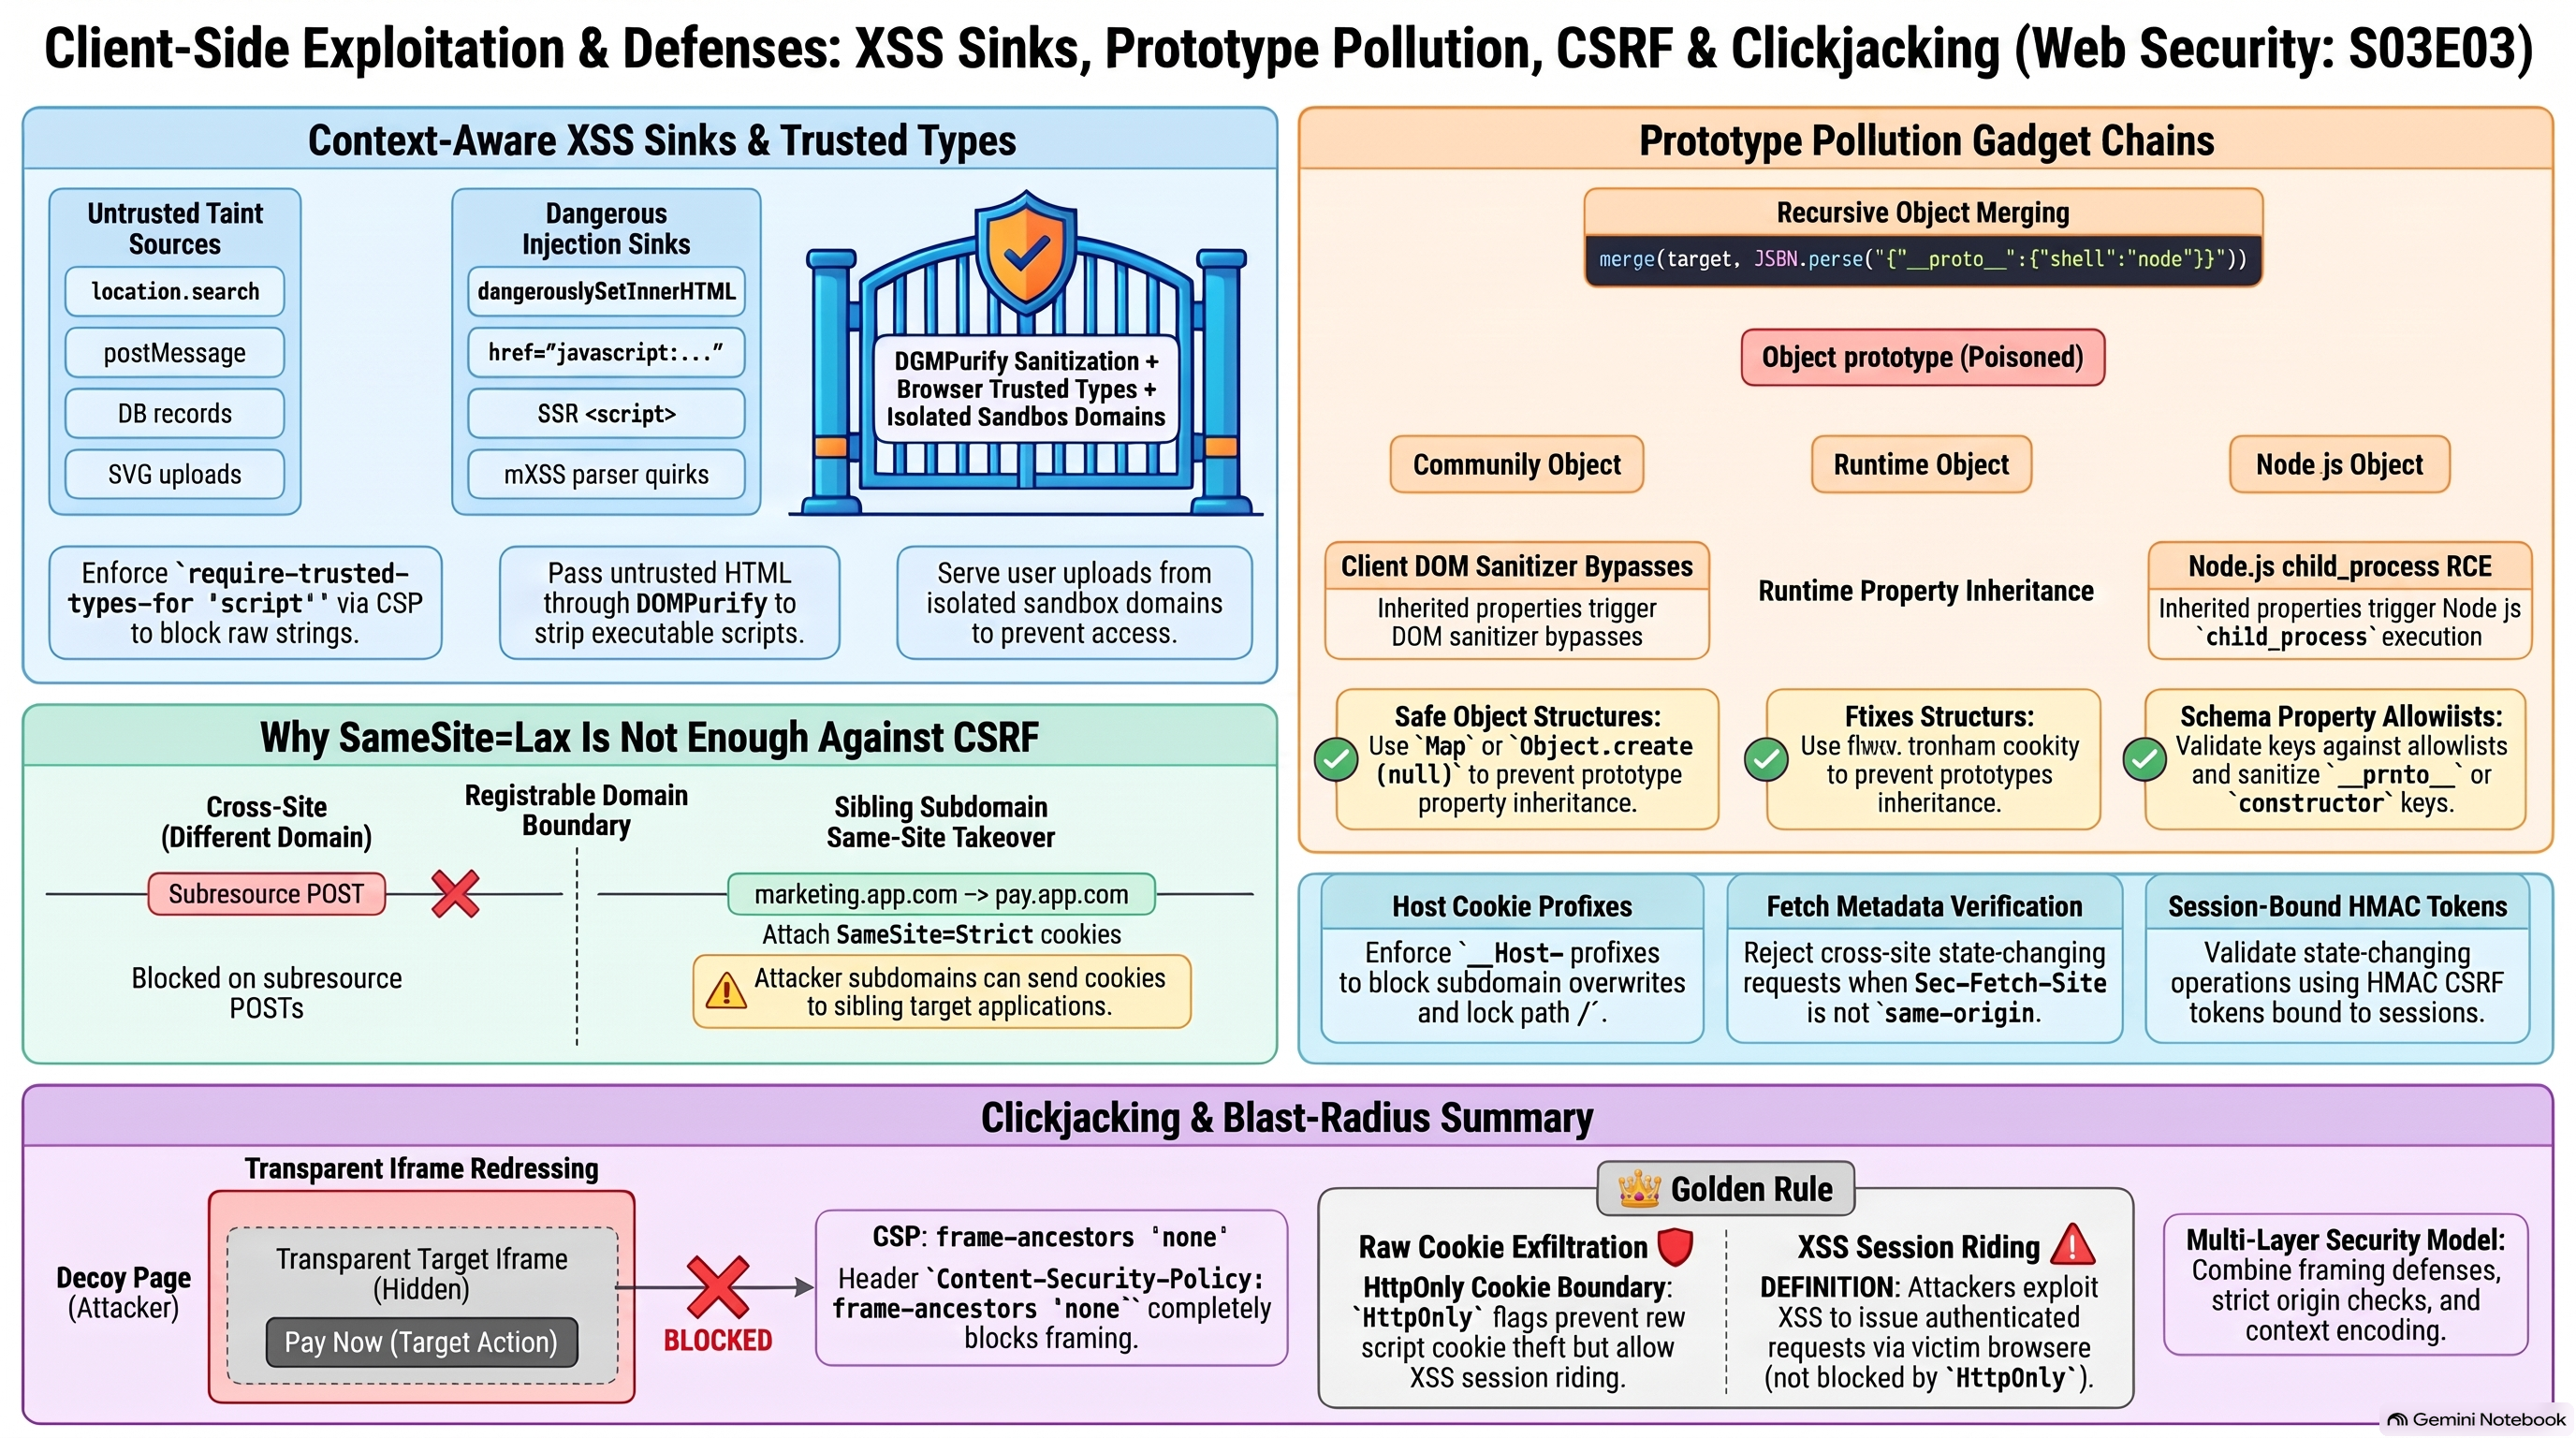
How cross-site scripting (XSS), CSRF and prototype pollution work, and why default defences still let them through.
Web Security
Videos (2)
Podcasts (1)
Slide decks (1)
Infographics (1)
Sources (9)
- web page Clickjacking Defense - OWASP Cheat Sheet Series
- web page Cross Site Scripting Prevention - OWASP Cheat Sheet Series
- web page Cross-Site Request Forgery Prevention - OWASP Cheat Sheet Series
- web page DOM based XSS Prevention - OWASP Cheat Sheet Series
- web page DOM-based vulnerabilities | Web Security Academy
- web page What is CSRF (Cross-site request forgery)? Tutorial & Examples | Web Security Academy
- web page What is Clickjacking? Tutorial & Examples | Web Security Academy
- web page What is cross-site scripting (XSS) and how to prevent it? | Web Security Academy
- web page What is prototype pollution? | Web Security Academy